Anduril
Well-known member

- Windows PC, preferably with 8GB RAM minimum
- Interest in malware analysis or reverse engineering
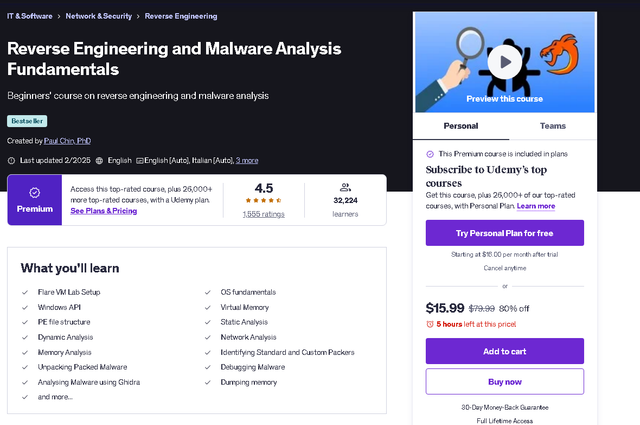
DescriptionIf you are completely new to reverse engineering and malware analysis, then this course is for you. I will take you from zero to proficient level in reverse engineering and analyzing malware. You will learn using plenty of practical walk-throughs. We will learn the basics first then gradually proceed to more advanced topics. All the needed tools will be introduced and explained. By the end of this course, you will have the fundamentals of malware analysis under your belt to further your studies in this field. Even if you do not intend to take up malware analysis as a career, still the knowledge and skills gained in reverse engineering and analysis would be beneficial to you to reverse software as well.
Everything is highly practical. No boring theory or lectures. More like walk-throughs which you can replicate and follow along. We will use tools like tridnet, bintext, pestudio, cff explorer, regshot, procdot, fakenet, wireshark, process monitor, process hacker, xdbg, Ghidra and more...
Topics include:
- Lab Setup
- Tools
- OS Fundamentals
- Virtual Memory and the PE file
- Windows Internals
- Malware Components
- Static analysis
- Dynamic Analysis
- Network Analysis
- Unpacking Standard and Custom packers
- Dumping memory
and more...
This course is suitable for:
- Anyone who has no background on malware analysis and just starting out in this field
- Hobbyist who just like to learn how to reverse engineer and analyze malware
- Students who like to get started on the career path to become malware analysts
- Hackers looking for additional tools and techniques to reverse software
The prerequisites:
Just a windows PC and an interest in malware analysis, or software reverse engineering.
Enroll now and I will see you inside. Thanks!
Who this course is for:
- Anyone who has no background on malware analysis and just starting out in this field
- Hobbyist who just like to learn how to reverse engineer and analyze malware
- Students who like to get started on the career path to become malware analysts
- Hackers looking for additional tools and techniques to reverse software
Hidden Content
https://pixeldrain.com/u/2ABMjrbK
PW: Anduril


